The Cyber Soldier Project is an advanced cyber resilience and training initiative developed for IT and SOC professionals.
Its primary goal is to enable them to rapidly develop offensive (Red Team) and investigative skills that are essential for effective incident response and post-incident forensics. These competencies allow organizations to better understand the methods used by cyber adversaries and to independently test the effectiveness of their cybersecurity systems — including EDR, SIEM, and XDR — through the execution ofrealistic, intelligence-based cyberattack simulations.
The project is based on cyber threat intelligence and developed in line with the European Framework for Threat Intelligence-Based Ethical Red Teaming (TIBER-EU).
A quick and effective response to cyber incidents helps organizations minimize or even prevent losses.
Incident management is now a regulatory requirement under frameworks such as NIS2, DORA, and GDPR.
The ability to identify and respond to cyber incidents is therefore essential for many roles across both IT and OT environments, including:
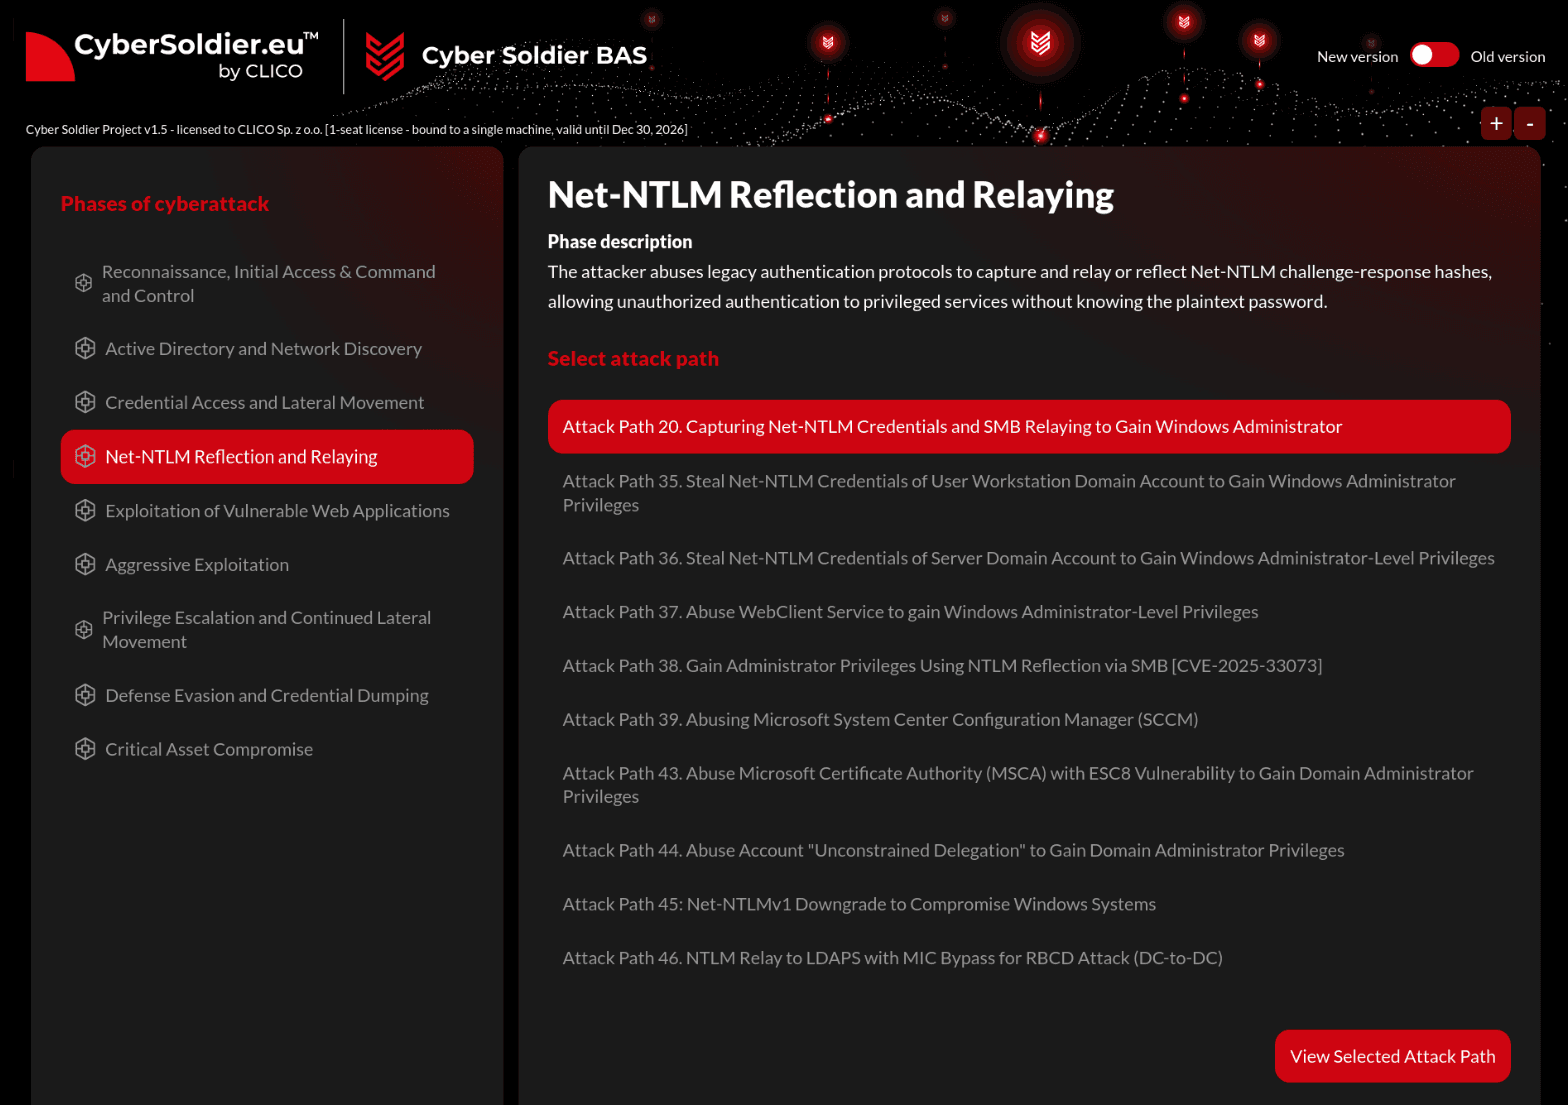
An educational and testing platform that allows users to safely execute realistic cyberattack scenarios based on verified threat intelligence data.
The BAS tool can be deployed both in production and in Cyber Range test environments, enabling the replication of actual adversary techniques for testing detection, observability, and response.
An intelligent module that automatically generates attack scenarios tailored to selected threat actors.
It leverages a database of pre-built attack paths from the Cyber Soldier BAS environment and selects techniques attributed to a chosen actor according to the MITRE ATT&CK framework and other cyber threat intelligence sources.
A dedicated training and testing environment that replicates real enterprise IT infrastructures, including:
A complementary framework used to verify whether cybersecurity systems operate correctly during simulated attacks.
It helps identify gaps in detection, misconfigurations, and blind spots, ensuring that defensive systems can effectively recognize both malicious and legitimate-like techniques used by real attackers.
Participants gain hands-on experience in an environment mirroring real-world infrastructures — including Active Directory, MS Exchange, SQL, CA, web servers, and Linux systems — protected by commercial EDR and SIEM solutions.
The Cyber Range is available both on-site at the CLICO training center and remotely 24/7.
The most effective way to strengthen incident response capabilities is through safe, controlled simulations of real cyberattacks within a company’s live network.
Using the Cyber Soldier BAS application, organizations can safely execute realistic attack chains and practice response procedures with their existing security stack — including EDR, NGFW, SIEM, and other monitoring tools.
The Cyber Soldier Project combines both offensive and defensive expertise, developed by a team of certified cybersecurity professionals with globally recognized credentials.
Unlike traditional training or CTF-style environments, Cyber Soldier is not a gamified simulation but a true intelligence-driven platform that reproduces real adversary tactics and techniques.
It guides users through every step of an actual cyber intrusion — from reconnaissance to exploitation and lateral movement — explaining both offensive logic and defensive countermeasures.
The result is a powerful environment for building internal Red Team capabilities and improving the overall digital resilience of the organization.
A project by CLICO © 1991-2026. All rights reserved.